Unmasking the Backend: Rapid Overview of PlugX/Korplug C2 Infrastructure
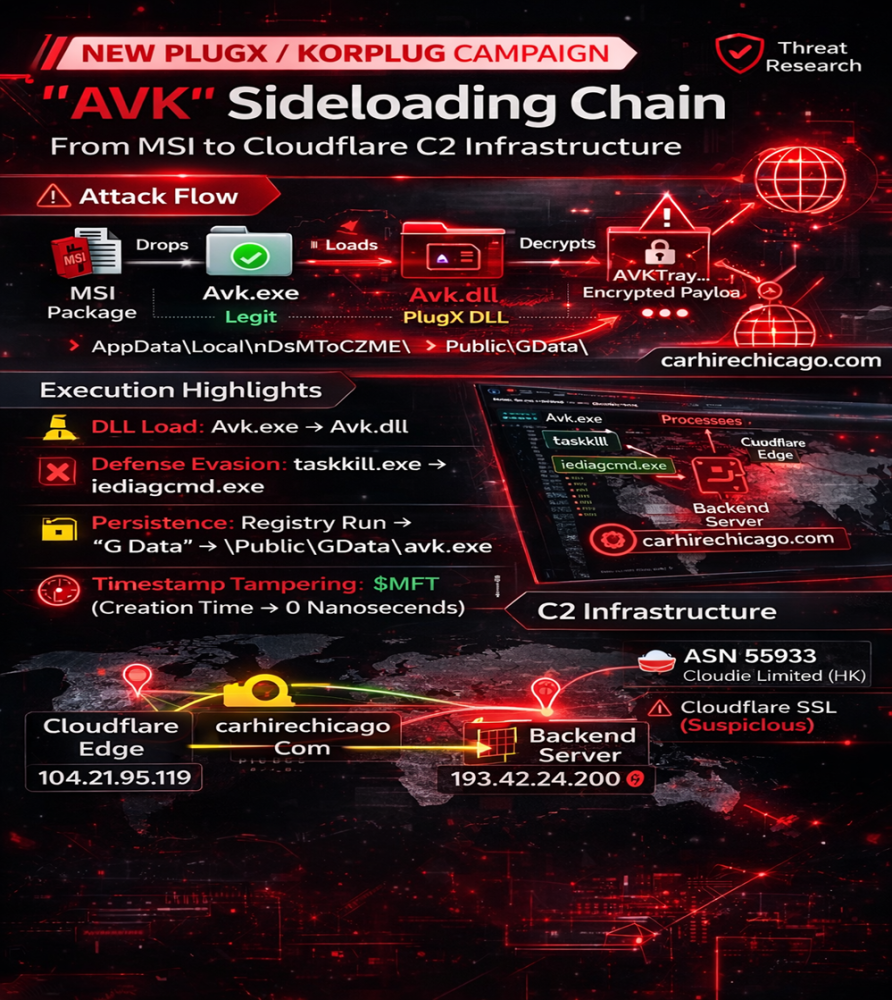
Overview Diagram
New plugx/korplug malware msi file (AB56563F3817E31568E487EDC232A7EE).
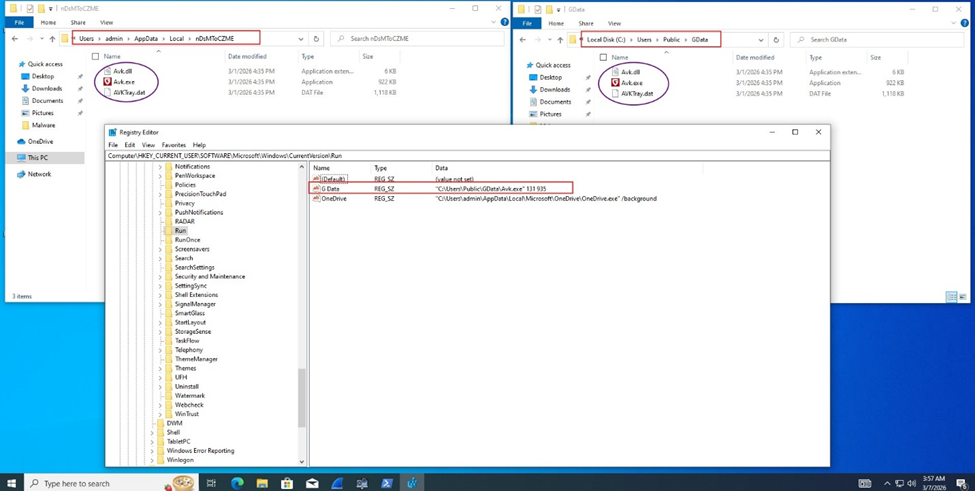
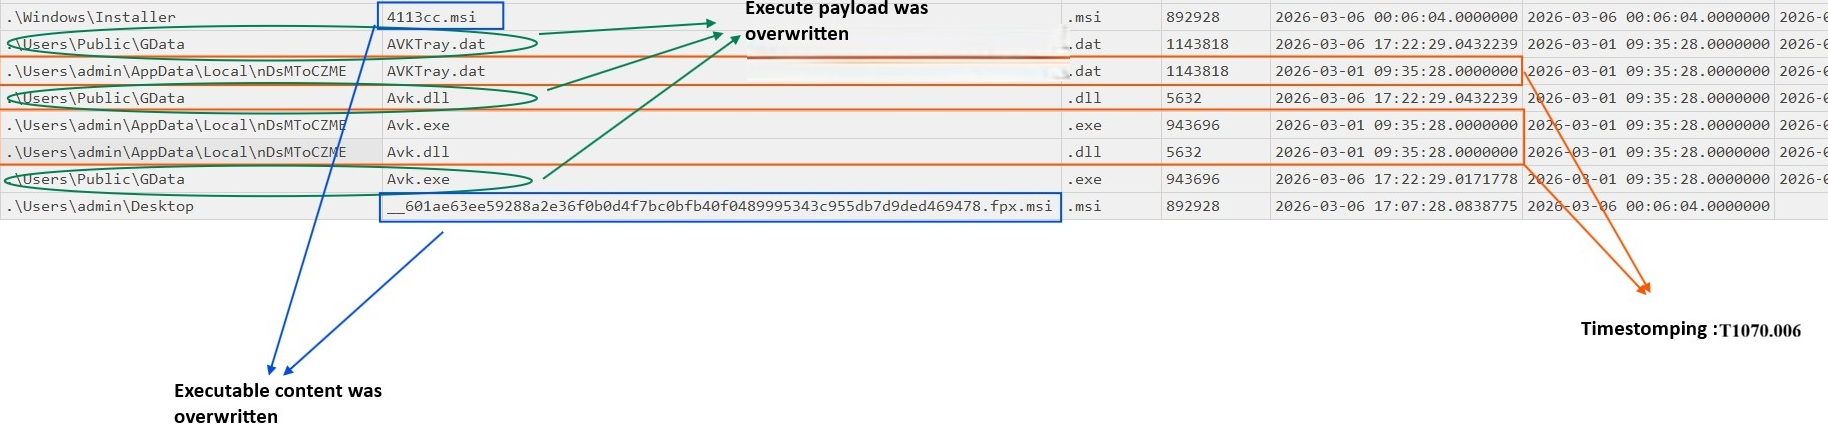
Execution of the MSI package resulted in the deployment of several components, including the legitimate G DATA executable (avk.exe), a PlugX DLL used for sideloading (avk.dll), and an encrypted payload file (AVKTray.dat). The files were placed within AppData and Public\GData directories, with persistence achieved via modification of the Windows Registry Run key (T1547.001).
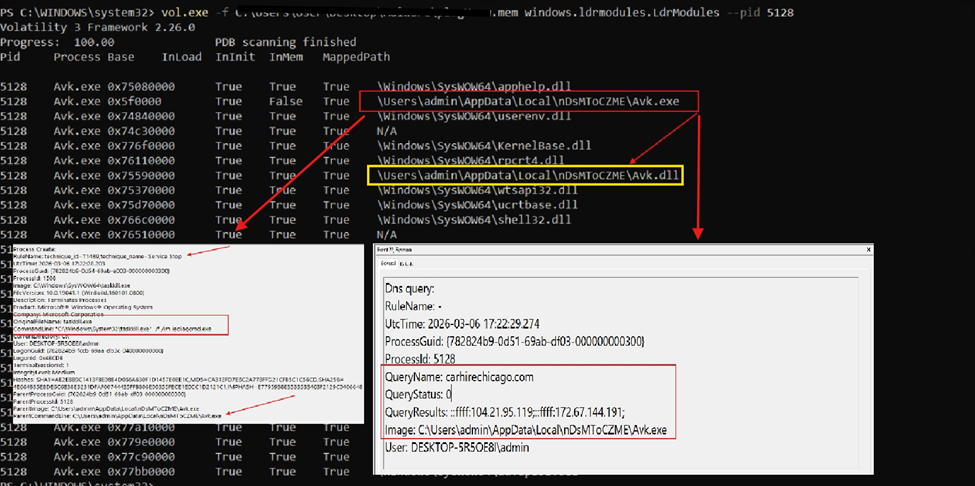
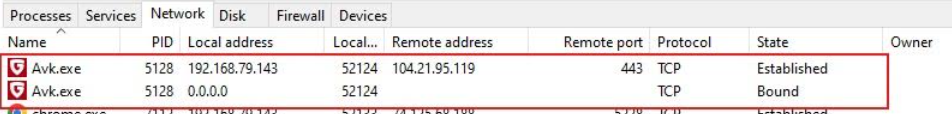
During execution, Avk.exe loaded the sideloaded DLL Avk.dll (T1574.001) from the same AppData\Local\nDsMToCZME directory. Shortly after the DLL was loaded, the process initiated a DNS query and subsequent network communication with the domain carhirechicago[.]com (T1071), which resolved to 104.21.95.119 within Cloudflare infrastructure. In the same execution chain, Avk.exe also spawned taskkill.exe to forcibly terminate iediagcmd.exe, potentially as a defense-evasion measure to reduce diagnostic visibility or prevent interference.
Analysis of the $MFT file indicated that the file creation timestamps for the deployed components contain nanosecond values set to zero, which may indicate timestomping (T1070.006) performed to evade forensic timeline analysis.
Investigation of Potential Backend Infrastructure Associated with the C2 Domain
DFIR analysis observed that the infected host communicated with Cloudflare edge IP addresses associated with the domain carhirechicago[.]com. To further investigate potential infrastructure related to the domain, additional threat intelligence analysis was conducted.
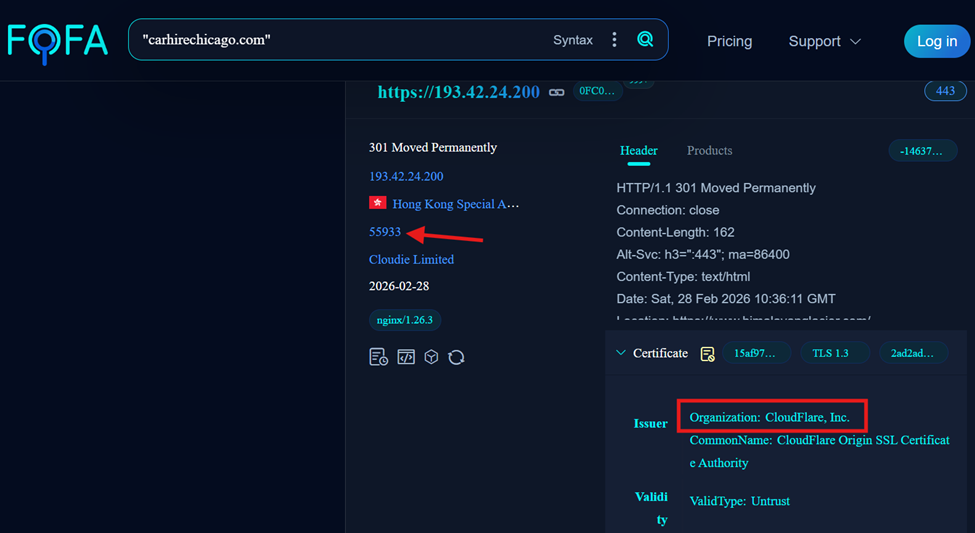
Using the FOFA search engine, carhirechicago[.]com was found resolving to the IP address 193.42.24.200, hosted by Cloudie Limited (ASN 55933, Hong Kong). The server’s SSL certificate lists the domain carhirechicago[.]com, despite the ASN not belonging to Cloudflare, which may indicate an unusual or potentially misleading configuration, suggesting possible exposure of backend infrastructure behind the Cloudflare edge.
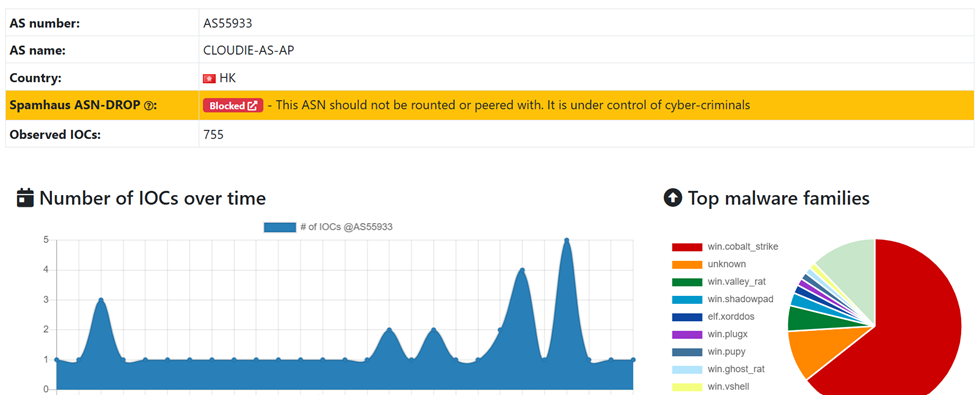
A review of ASN 55933 on ThreatFox indicates a high-risk profile, with historical associations primarily linked to Cobalt Strike malware infrastructure, suggesting the ASN is frequently leveraged by threat actors for command-and-control operations.
IOCs:
carhirechicago[.]com
AB56563F3817E31568E487EDC232A7EE - msi
9E77DEA40479ABF11FC3894BF50829F7 – avk.dll
E7CB954F4BBDBADBD2C0206577621683 – avk.exe
33BBFA6D5C8A1078E4E260E15D563360 - AVKTray.dat
193.42.24.200 (RELATED INFRASTRUCTURE)
YARA Rule
import "pe"
rule PlugX_Korplug_AVK_Sideload_Loader_DLL_avk_dll
{
meta:
author = "MM-Sherlock"
date = "2026-03-08"
description = "High-confidence detection for
PlugX/Korplug sideload loader DLL masquerading as avk.dll
(small DLL with specific exports/strings)"
family = "PlugX / Korplug"
reference = "Internal Research"
confidence = "high"
sample_md5_reported =
"9E77DEA40479ABF11FC3894BF50829F7"
strings:
$exp_mod = "ModuleMain" ascii
$dllmain = "__DllMainCRTStartup@12" ascii
$dos = "This program cannot be run in DOS mode." ascii
$u1 = "sDl.dll" ascii fullword
$u2 = "Qj@RSj" ascii
$u3 = "C0T0e0v0" ascii
$u4 = "||||~<|" wide
condition:
uint16(0) == 0x5A4D and
pe.is_dll and
filesize < 25KB and
pe.exports($exp_mod) and
( $dllmain and $dos and 2 of ($u*) ) or
( $dos and 3 of ($u*) )
)
}
rule Context_GDATA_AVK_EXE_BuildPath_LoaderPDB_HuntOnly
{
meta:
author = " MM-Sharlock "
date = "2026-03-08"
description = "Hunt-only: avk.exe binary containing
specific build path Loader.pdb. Use for correlation with
malicious avk.dll/AVKTray.dat."
confidence = "medium"
sample_md5_reported =
"E7CB954F4BBDBADBD2C0206577621683"
strings:
$pdb = "C:\\j\\workspace\\_AppDev_avk_release_1-
production\\bin\\Release32v14x\\Loader.pdb" ascii
$avk = "AVK.dll" wide
$gdata = "@G DATA CyberDefense AG 'AVK.exe" wide
condition:
uint16(0) == 0x5A4D and
pe.is_pe and
filesize < 3500KB and
$pdb and
( $avk or $gdata )
}KQL
DeviceRegistryEvents
| where ActionType == "RegistryValueSet"
| where RegistryKey contains
@"\Software\Microsoft\Windows\CurrentVersion\Run"
| where RegistryValueName contains "G Data"
| where RegistryValueData has_all ("\\Public\\GData\\",
"avk.exe")
DeviceImageLoadEvents
| where FolderPath contains @"\AppData\Local"
| where FileName endswith "avk.dll"
| where InitiatingProcessFileName contains "avk.exe"
| project TimeGenerated, DeviceName, FolderPath, FileName,
InitiatingProcessCommandLineRapid Investigation by Kyaw Pyiyt Htet (Mikoyan) and PHYO PAING HTUN ChiLai
#plugX