PlugX Loader and Payload Analysis: Persistence, Process Injection and C2 Infrastructure
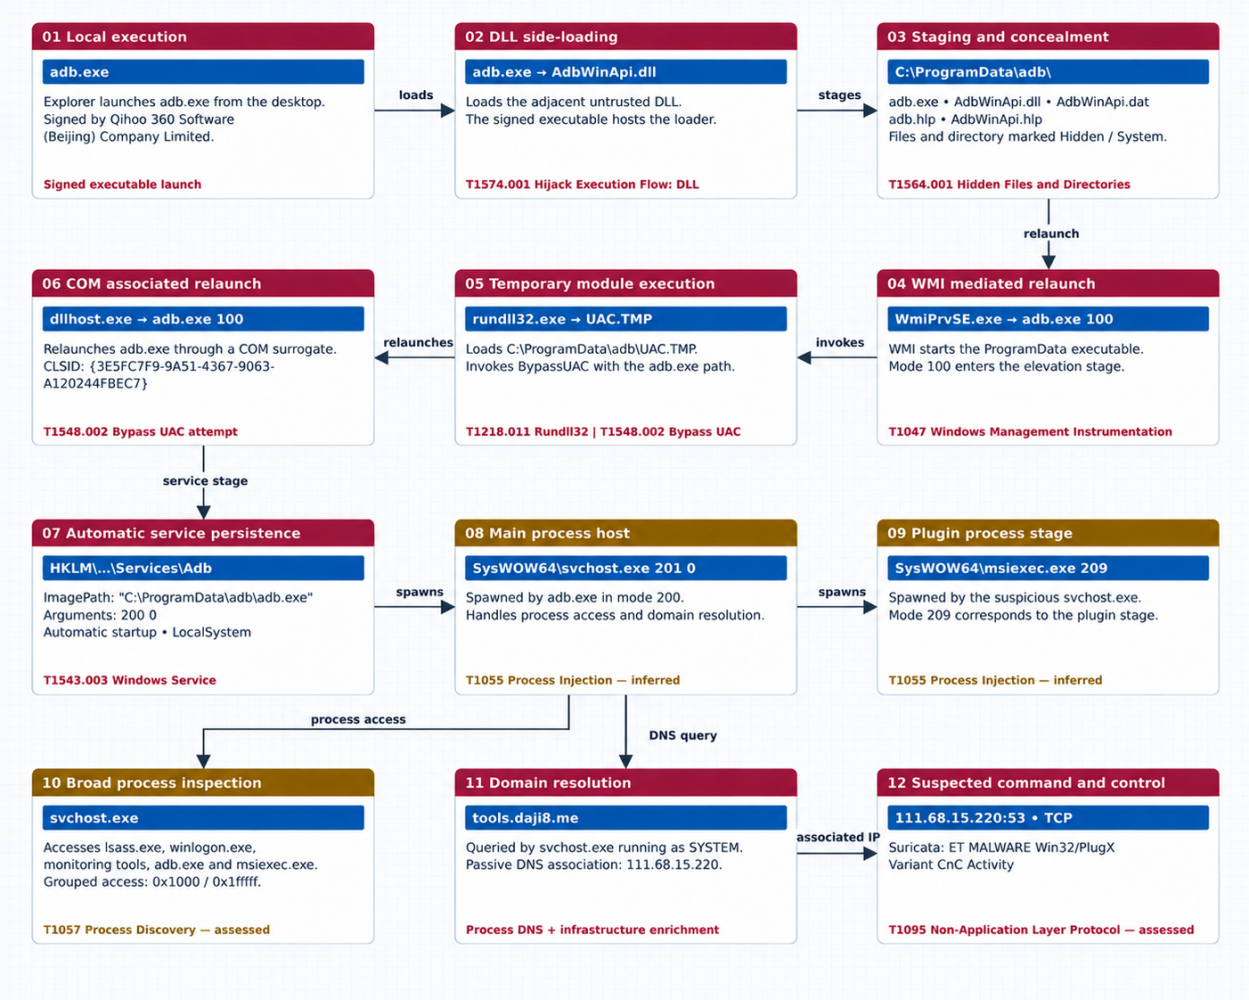
Attack Flow
The execution chain progresses from the desktop loader through ProgramData staging and privilege escalation to service execution, as illustrated below.
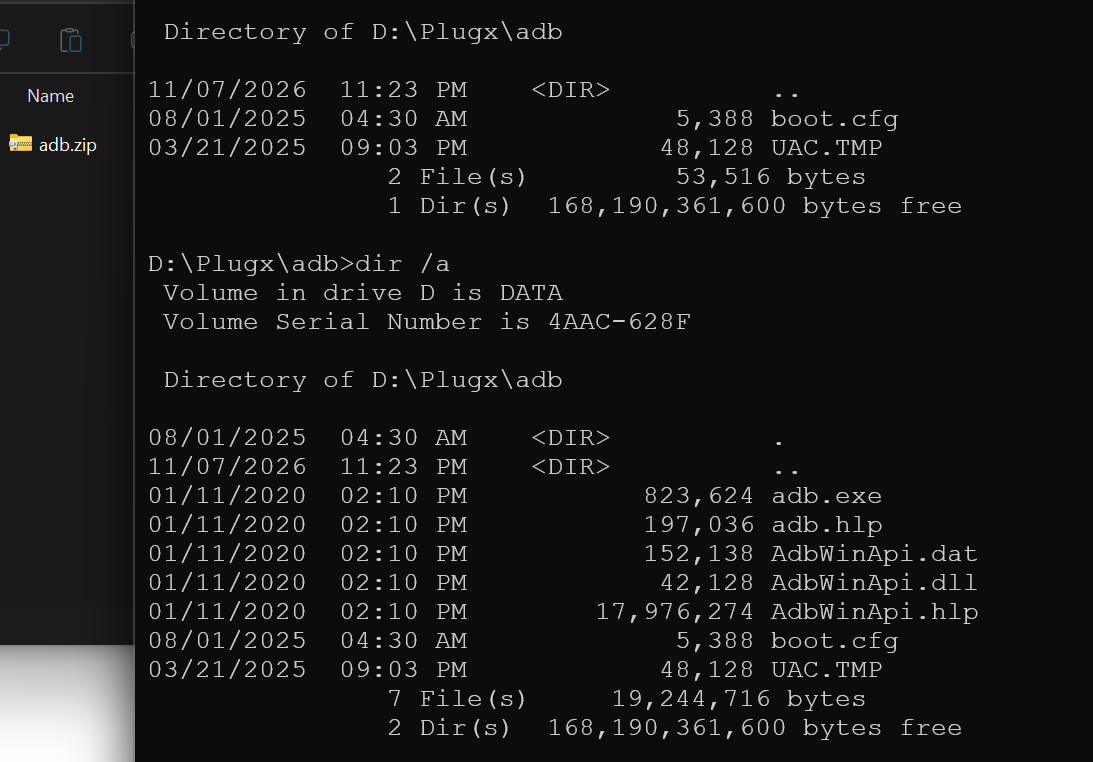
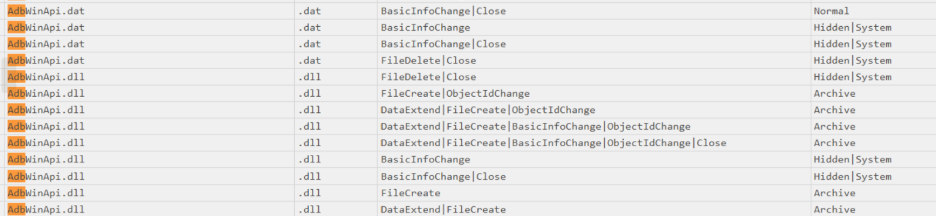
Hidden and System File Attributes
An adb.zip archive containing a suspected PlugX sample has been acquired for deep dive analysis. Following extraction of zip, the PlugX companion files (AdbWinApi.dat, AdbWinApi.dll, and AdbWinApi.hlp) were concealed by applying Hidden and System attributes, making them invisible in normal Windows Explorer views.
| Component | Description | Function / Role |
|---|---|---|
| adb.exe | Digitally signed by Qihoo 360 Software | Legitimate executable abused as the DLL side-loading host |
| AdbWinApi.dat | Encrypted PlugX shellcode | Stores encrypted shellcode used in the subsequent execution chain |
| AdbWinApi.dll | PlugX loader | Loads and processes the encrypted payload |
| uac.tmp | DLL with UAC bypass capability | Facilitates privilege escalation |
| boot.cfg | C2 Configuration | Stores encrypted C2 communication configuration for subsequent decryption |
Execution
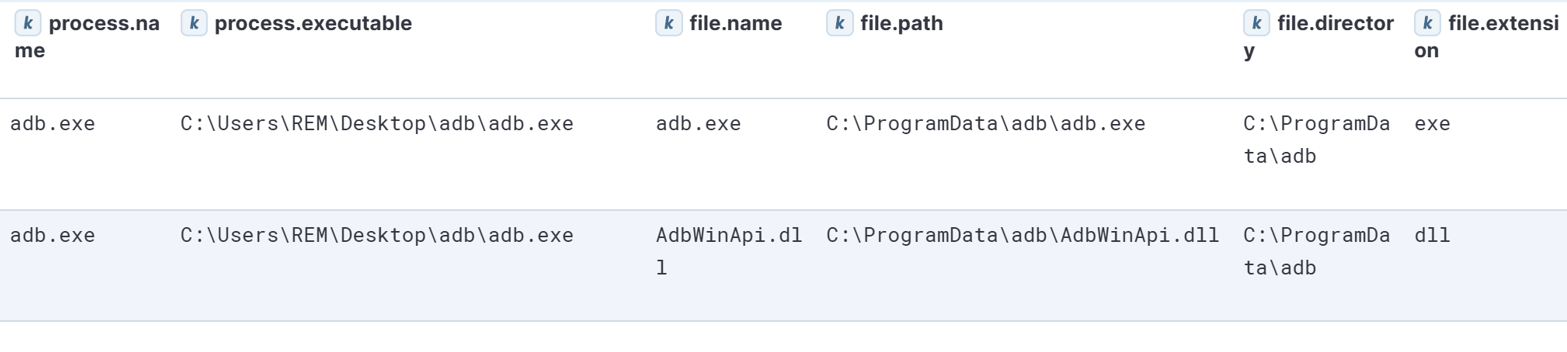
The execution of adb.exe resulted in the creation of component artifacts within C:\ProgramData\adb, as captured by Sysmon file creation logs.
DLL SideLoading
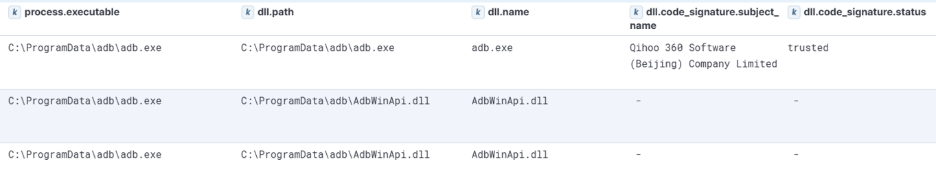
The signed adb.exe, which loads an untrusted, application-local AdbWinApi.dll. The same DLL side-loading behavior is observed again after staging under C:\ProgramData\adb.
Privileges Escalation
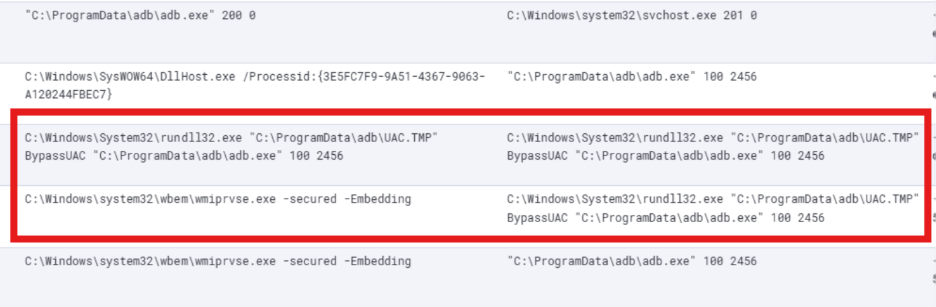
The binary invokes rundll32.exe to load UAC.TMP (a masquerading DLL file) and call its BypassUAC export, passing the sample’s own command line (adb.exe 100 2456) as the argument. The command line is re-executed with elevated privileges so the next stage can install persistence. Mode 100 selects the install and persistence routine, and 2456 is the PID of the parent adb.exe that started the process.
Process Injection
When launched with the argument 200, adb.exe creates %SystemRoot%\system32\svchost.exe suspended with the command line svchost.exe 201 0 and injects its payload into it; the missing -k service group is unusual for a legitimate svchost.exe.
The injected svchost.exe then creates msiexec.exe 209 <PID> in each logged-on user session using a duplicated user token (<PID> is the parent svchost.exe), and injects the same payload into it.
adb.exe
└─> adb.exe 200 0                 (parent command line)
   └─> svchost.exe 201 0          (child command line;
suspended and injected)
     └─> msiexec.exe 209 <PID>    (child command line;
created per user session and injected)
Execution Mode
100 - Bypass UAC
200 - Injector / launcher
201 - Main RAT
209 - Per-user-session helperPersistence Mechanism
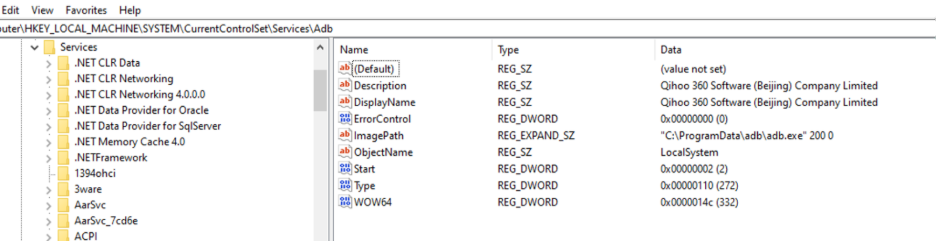
The malware establishes persistence by creating or modifying a Windows service registry entry under HKLM\SYSTEM\CurrentControlSet\Services\Adb.
Command & Control
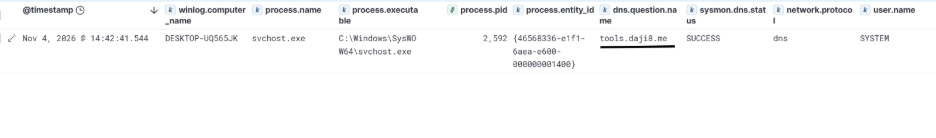
The primary svchost.exe stage queried tools.daji8[.]me while executing under the SYSTEM account. The successful DNS resolution links the domain to the same process exhibiting extensive process access activity.
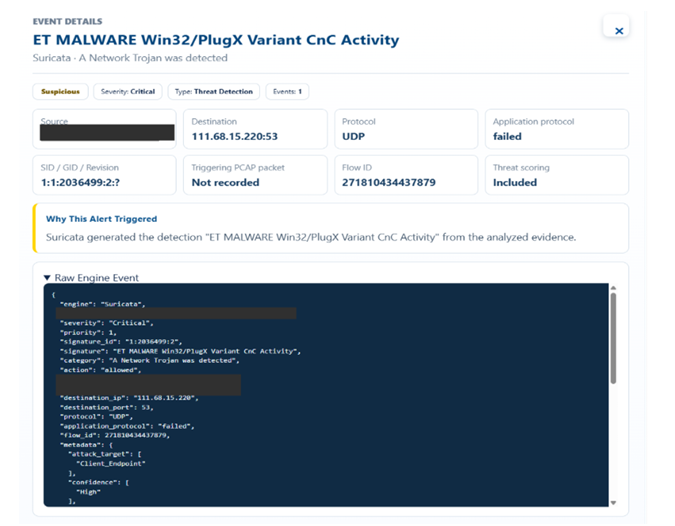
A Network Intrusion Analyzer alert for "ET MALWARE Win32/PlugX Variant CnC Activity" was triggered by traffic to tools.daji8[.]me (resolving to 111.68.15[.]220). As shown below, this Suricata alert directly validates the PlugX indicator of compromise (IOC) discovered during our host-level forensic analysis.
PlugX Code Analysis Section
PlugX Configuration Extraction
The PlugX loader invokes sub_10004790 to open boot.cfg, retrieve its file size, and read the encrypted contents into memory for subsequent decryption and processing.
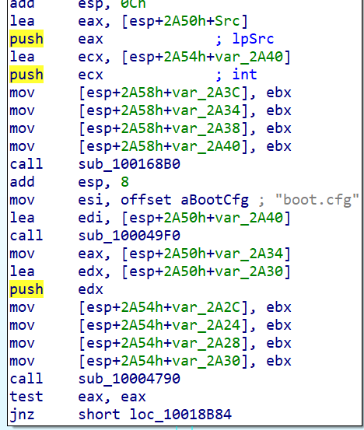
#ReadFile operation (sub_10004790)
mov     edx, [ebp+arg_0]
push    eax             ; lpOverlapped
mov     eax, [edx+4]
lea     ecx, [ebp+NumberOfBytesRead]
push    ecx             ; lpNumberOfBytesRead
push    edi             ; nNumberOfBytesToRead
push    eax             ; lpBuffer
push    ebx             ; hFile
call    ds:ReadFile
test    eax, eax
jnz     short loc_100047FF
#Retrieval of the 4-byte decryption key from the embedded
config and call to the decryption routine
loc_10018A86:
mov eax, [edi]
push 150Ch
push edi
lea ecx, [esp+2A58h+var_2A20]
call sub_10008760
test eax, eax
jnz short loc_10018A3DDecryption routine of the PlugX config
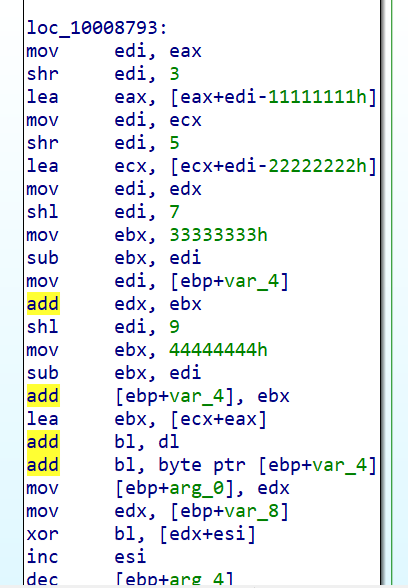
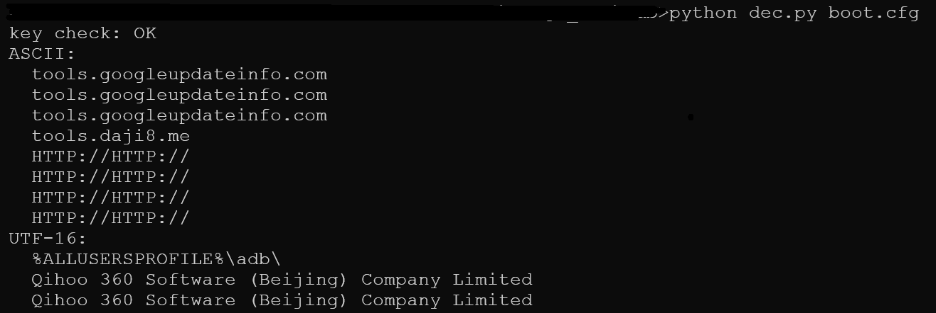
As shown below, decryption of the PlugX configuration payload successfully revealed the embedded C2 address:
PlugX – C2 Infrastructure Correlation & External Intelligence Assessment
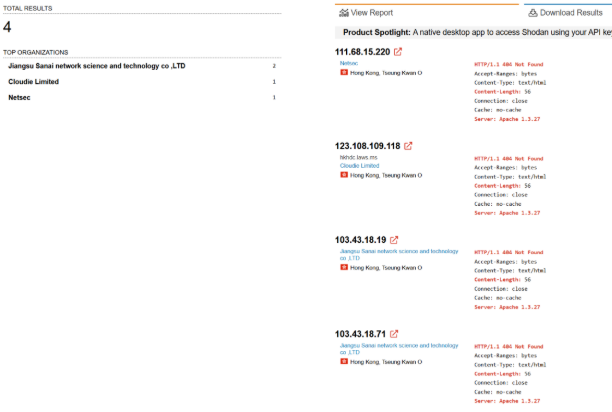
The HTTP header fingerprint of 111.68.15[.]220 was used as a pivot for Shodan searches, identifying three additional IP addresses exhibiting the same HTTP header pattern and expanding the investigation into a four-IP C2 infrastructure cluster.
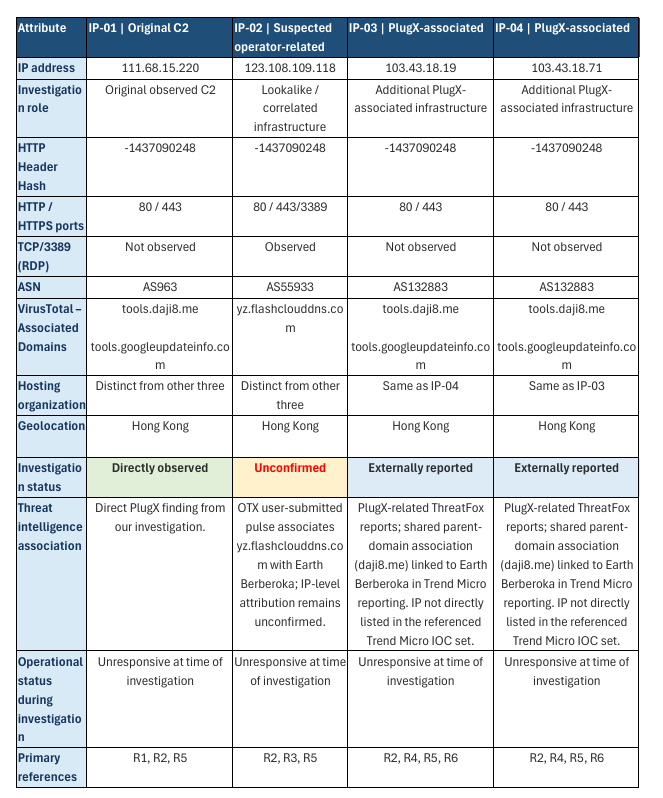
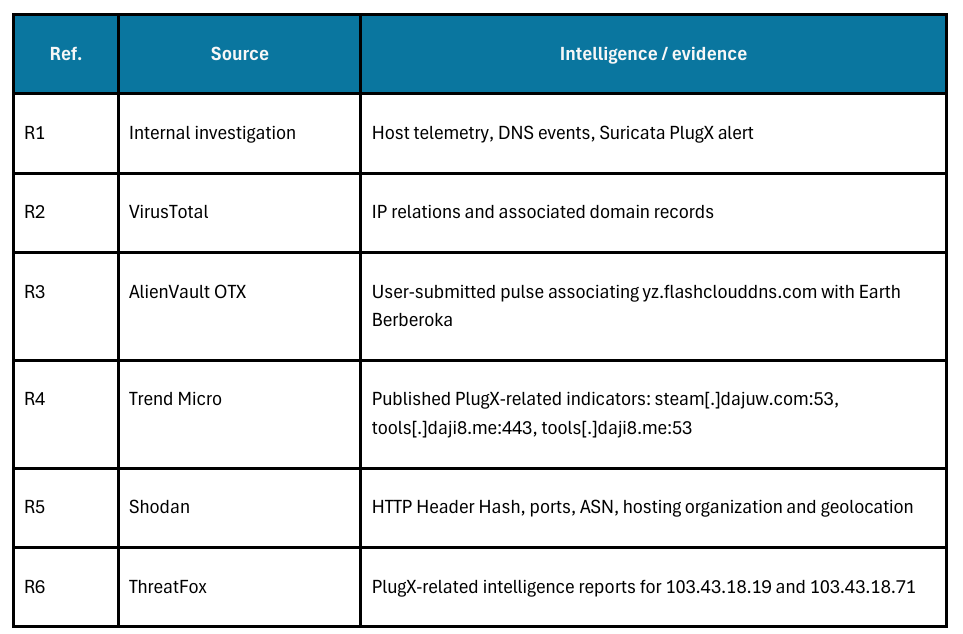
Assessment: We assess with moderate confidence that 111.68.15.220 is likely part of infrastructure used by Earth Berberoka.
Biases: We observed this host serving a PlugX payload. It shares HTTP header hash -1437090248 and the parent-domain association (daji8[.]me) with infrastructure reported by Trend Micro as linked to Earth Berberoka.
Gaps: The IP does not appear in the Trend Micro IOC set, the lookalike IP’s attribution rests on a single unverified OTX pulse, and all hosts were unresponsive, which prevented further collection.
Appendix
Indicator of Compromise
| Artifact | Type | Indicator |
|---|---|---|
| Adb.exe | SHA-256 | ef4c7f4c417c18cd3394dd81ccd94381af252e0af81b0ad89b7e6d81412f4706 |
| Adb.dat | SHA-256 | 88045766007380b99fa7874c633d66bcb17d3314b6145ad5f8d8216e8e24b375 |
| UAC.TMP | SHA-256 | b3d819160421011c002e1c4bd2621b15566134937e700697258eba954de5836b |
| AdbWinApi.dll | SHA-256 | 35311bb7becba40d1fd99414cc1d14db837630e3ea13804442698b777476fe76 |
| Boot.cfg | SHA-256 | A0130462172EF03869349D9FFF564E9F66A76F31FCCEDED5D7AE5F9C64C42563 |
| C2 domain | Domain | tools[.]daji8[.]me |
| C2 address | IPv4 | 111.68.15.220 |
MITRE Mapping
T1574.001 - Hijack Execution Flow DLL
T1047 - Windows Management Instrumentation
T1218.011 - Rundll32
T1112 - Modify Registry
T1548.002 - Bypass User Account Control
T1543.003 - Windows Service
T1564.001 - Hidden Files and Directories
T1055 - Process Injection
T1057 - Process Discovery
T1095 - Non Application Layer Protocol
KQL
PlugX Persistence via Adb Service Registry Modification
DeviceRegistryEvents
| where (RegistryKey contains "HKLM\\System\\CurrentControlSet\\Services\\Adb" and RegistryKey contains "ImagePath") and RegistryValueData contains "ProgramData\\adb\\adb.exe"
PlugX UAC Bypass via Rundll32 Loading TMP With BypassUAC Export
DeviceProcessEvents
| where (FolderPath endswith "\\rundll32.exe" or ProcessVersionInfoOriginalFileName =~ "RUNDLL32.EXE") and (ProcessCommandLine contains "BypassUAC")
PlugX DLL Sideloading - Untrusted AdbWinApi.dll Loaded From ProgramData
DeviceImageLoadEvents
| where FolderPath endswith "\\AdbWinApi.dll" and FolderPath contains "ProgramData\\adb"
Disclaimer: This research was performed independently and in our personal capacity. It does not represent the views of employer, past or present, or of any affiliated organization, and no confidential or proprietary information from any employer was used. The findings are provided for informational and defensive purposes only, “as is”, without warranty. Some conclusions are based on static analysis and may be revised as more information becomes available.